Hospital price transparency
An internal sign-off workflow for attestation
The attester signs; the institution prepares. CMS expects the named official to be able to consult the people closer to the file - a compliance officer, a revenue cycle leader - before attesting. A workflow makes that consultation real instead of hoped for.
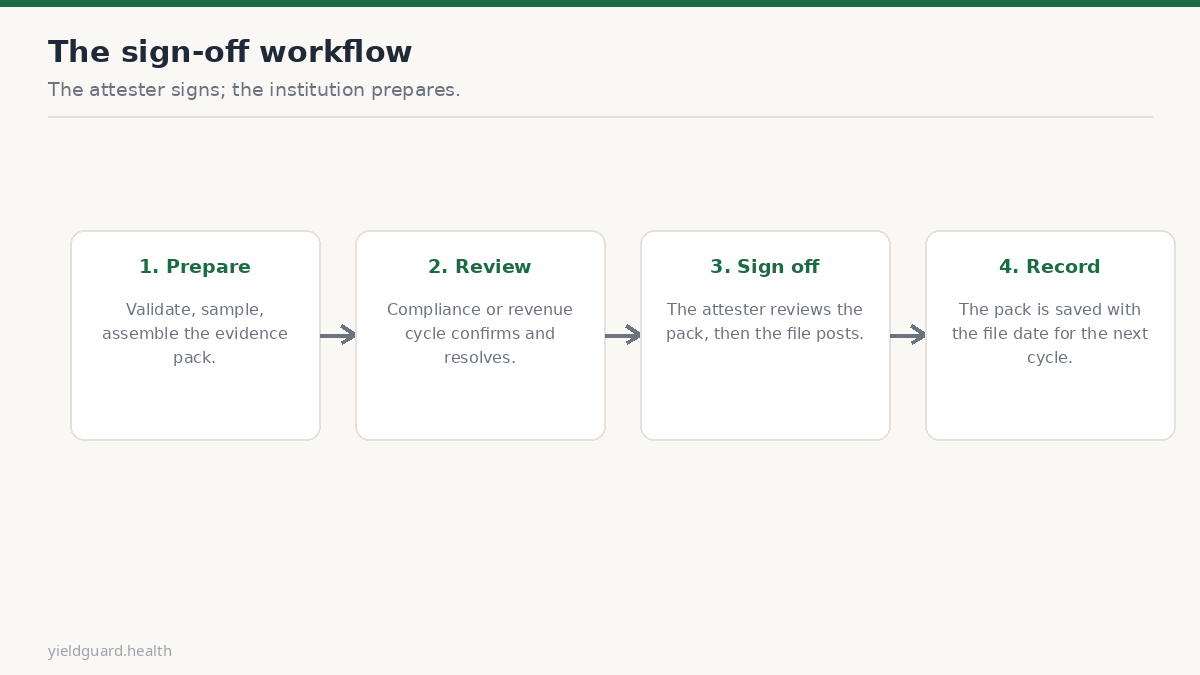
A workable shape has four steps. First, preparation: the team that owns the file runs the validator, samples the data, and assembles a short evidence pack - what was checked, what was found, what was fixed. Second, review: the compliance officer or revenue cycle leader confirms the pack and resolves open questions. Third, sign-off: the attester reviews the same pack, not just the file, and the affirmation posts with it. Fourth, the record: the pack is saved with the file's date, so the next review starts from evidence instead of memory.
Keep the pack small on purpose. A one-page record of checks run, rows sampled and issues closed is enough to support the signature - and it is exactly what a certification request would ask for.
The workflow is the difference between an attester who believes the file and an attester who hopes.
Sources
Related guides
YieldGuard audits hospital machine-readable files against the current CMS requirements. Request Compliance Assessment